
BuildMEP process-safety field guide
Use two major tank-farm incidents to test whether level control, leak detection, alarm response and emergency isolation form a working protection system rather than a collection of installed devices.
Decision brief: verify the complete response chain
A detector does not control a release by itself. The design must detect the initiating failure, produce an actionable alarm, isolate the inventory from a safe location and remain available after testing or maintenance.
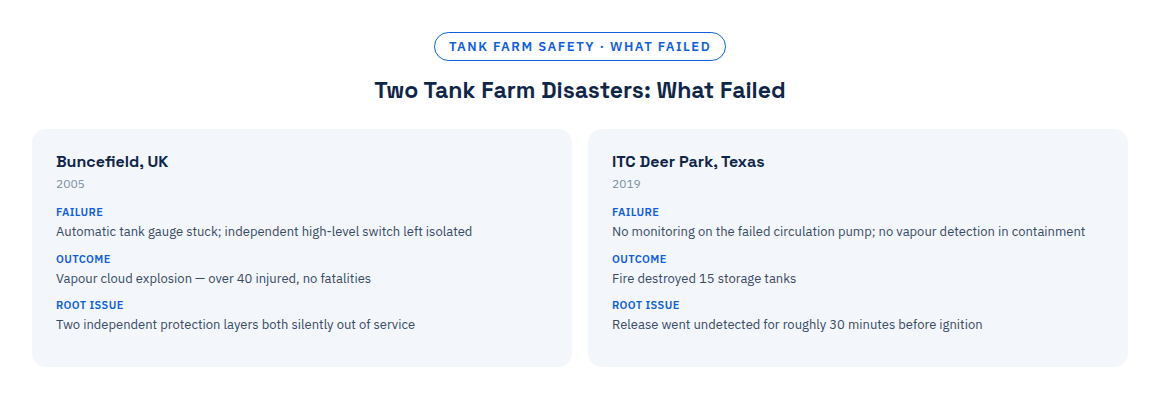
- Buncefield: the normal level indication and the independent high-level protection both failed to prevent an overfill.
- ITC Deer Park: a pump release continued for about 30 minutes without flammable-gas detection, and the tank inventory could not be remotely isolated.
- Engineering test: for every credible release, identify the detection point, alarm recipient, response time, shutdown action, final isolation element and proof-test method.
The shared failure chain
The practical lesson is not to specify every technology shown in this chain. It is to trace each credible scenario from release to safe state and expose any point where the assumed protection depends on an unavailable instrument, an unverified alarm or a manual action that cannot be completed safely.
Buncefield: installed protection was not available protection
During the night of 10-11 December 2005, unleaded petrol was transferred into Tank 912 at the Buncefield oil storage depot in Hertfordshire. The automatic tank gauge stopped following the rising level. The independent high-level protection also failed to stop the transfer, so petrol overflowed, a large vapour cloud formed and a major explosion occurred.
The UK Health and Safety Executive (HSE) records more than 40 injuries, no fatalities, extensive off-site damage and a fire that burned for several days. Five companies were later ordered to pay almost GBP 10 million in combined fines and costs.
The proof-test trap
HSE’s safety alert explains that the relevant high-level switch could appear to operate during a simulated test yet remain inoperative in normal service if its test lever or plate was not returned and locked correctly. A test that proves only the sensor mechanism is incomplete; the check must confirm the device is restored to service and that the alarm, trip and final shutdown path operate as intended.
What to verify on an overfill safeguard
- The independent high-high trip does not share a failure-prone signal, power source or logic path with the basic level-control system.
- Proof testing exercises the complete safety function, records the result and confirms removal of every test override, bypass and mechanical test device.
- A failed or frozen level indication creates a recognizable diagnostic condition rather than a believable but stale value.
- Transfer can be stopped within the available response time, including valve travel, pump shutdown and communication delays.
ITC Deer Park: the release was neither detected nor remotely isolated
On 17 March 2019, the circulation pump serving Tank 80-8 at the Intercontinental Terminals Company terminal in Deer Park, Texas, failed and released butane-enriched naphtha. The U.S. Chemical Safety and Hazard Investigation Board (CSB) found that the product continued to escape for about 30 minutes before the vapour ignited.
Tank 80-8 and its associated manifold area had no flammable-gas detection system to warn the control room. The tank farm also lacked remotely operated emergency isolation valves capable of stopping the release from a safe location. The fire burned for three days, spread to 14 additional tanks and destroyed all 15 tanks in the containment area.
The CSB identified five connected safety issues: pump mechanical integrity, flammable-gas detection, remotely operated emergency isolation, tank-farm layout and containment, and gaps in process-safety regulatory coverage. Its recommendations required more than adding detectors: they also addressed pump condition monitoring, alarm response and training, fail-closed remote isolation, and evaluation against the specifically cited editions of API Standard 2610 and NFPA 30.
Detector placement must follow the release scenario
The CSB report identifies pumps, seals, flanges and other common leak locations as important detection targets. It also notes that heavier-than-air flammable vapours commonly collect near grade or at low points. These are design inputs, not a universal mounting rule: product properties, release pressure, wind, congestion, drainage, dike geometry and detector technology still require a project-specific coverage study.
Buncefield and ITC compared
| Control point | Buncefield, 2005 | ITC Deer Park, 2019 | What the engineer should verify |
|---|---|---|---|
| Initiating event | Tank overfill during product transfer | Circulation-pump failure and loss of containment | Release scenarios include filling, circulation, transfer, drainage and maintenance states. |
| Primary indication | Automatic tank gauge stopped tracking the rising level | No effective pump condition indication warned of the developing failure | Stale, implausible and out-of-range signals generate a diagnostic response. |
| Independent detection | High-level protection did not trip in service | No flammable-gas detection near Tank 80-8 and its manifold | The backup layer is independent, correctly located, available and proof-tested. |
| Isolation | Transfer continued until overflow | Inventory could not be remotely isolated from a safe location | The shutdown action reaches a defined safe state within the available response time. |
| Escalation control | Vapour cloud formed outside the tank | Fire spread through a common containment area | Spacing, drainage, subdivisions, firewater and containment are checked as one system. |
A seven-step review for tank farms and fuel systems
- Define the credible release cases. Include overfill, pump and seal failure, flange or hose leakage, blocked drainage, wrong valve lineup and maintenance bypasses.
- Separate control from protection. Identify the basic control loop, independent high-high or shutdown function, leak or gas detection, emergency isolation and containment. Do not count one device twice.
- Map detector coverage. Base placement and technology on release points, vapour behaviour, ventilation, wind, obstructions, low points and the time available before ignition or off-site impact.
- Write the cause-and-effect response. State who receives each alarm, the first action, the automatic trip, the remote isolation command and the conditions for escalation or evacuation.
- Check the final element. A working sensor cannot compensate for an unavailable shutdown valve, a non-fail-safe actuator, an inaccessible manual valve or a pump that continues feeding the release.
- Proof-test end to end. Exercise the sensor, logic, alarm, trip, valve or pump response and feedback indication. Record restoration to normal service.
- Control impairments. Every bypass or out-of-service safeguard needs authorization, a visible register, temporary risk reduction, a restoration deadline and handover between shifts.
Do not copy the incident recommendations without a hazard review
The CSB recommendation to ITC cited the Third Edition of API Standard 2610 and the 2021 edition of NFPA 30 for that facility evaluation. Those references document the investigation’s basis; they do not automatically define the governing edition or full design basis for another site. Confirm the adopted law, authority requirements, product inventory, area classification, environmental conditions and current standard editions for the project.
Design and maintenance handoff checklist
- Current tank, pump, valve and transfer-line inventory
- Credible release and overfill scenarios documented
- Independent protection layers identified without double counting
- Detector coverage study tied to actual release locations
- Alarm setpoints and delay logic justified
- Cause-and-effect matrix approved and tested
- Remote isolation available from a safe location
- Value fail position and feedback proven
- Proof-test method includes restoration checks
- Bypass and impairment register reviewed each shift
- Temporary safeguards defined for unavailable protection
- Drills confirm operators can act within the required time
- Containment and drainage account for firewater and foam
- Changes pass management-of-change review
Apply the lesson beyond a tank terminal
The same logic applies at smaller scale to generator fuel systems, day tanks, diesel transfer pumps, chemical stores and plant-room sumps. Start with the release scenario, then verify detection, alarm, isolation and restoration. A device on a drawing is not a protection layer until its complete function is available, tested and connected to an executable response.
Related BuildMEP guidance
- Hydrocarbon leak sensors: selection and application guide
- Combustible gas detectors: field failure modes and reliability checks
Evidence trail
- UK Health and Safety Executive: Buncefield incident, reports and research.
- HSE safety alert HID 6-2010: high-level switch installation, testing and restoration.
- Buncefield Major Incident Investigation Board report.
- U.S. CSB: ITC Deer Park investigation, recommendations and report links.
- U.S. CSB final investigation report, released 6 July 2023.
Evidence boundary: This guide draws transferable engineering checks from two investigations. It is not a site-specific hazardous-area design, detector coverage study, LOPA, SIL determination or code-compliance certificate.
Frequently asked questions
Is a high-high level switch enough to prevent overfill?
No. It must be independent of the basic level-control failure being protected against, connected to an effective shutdown action, proof-tested through the final element and demonstrably restored after testing.
Should every tank farm use the same gas-detector layout?
No. Detector technology and placement depend on the stored product, credible leak locations, release rate, ventilation, wind, congestion, dike and drainage geometry, alarm objective and response time.
Why is remote isolation treated separately from detection?
Detection creates information; isolation limits the inventory feeding the event. If the only isolation point requires a person to approach a flammable release or fire, the response may be unsafe or too slow.
What is the most important maintenance record?
No single record is sufficient. The critical evidence is an end-to-end test history showing the sensor, logic, alarm, trip and final element worked, followed by confirmation that all bypasses and test devices were returned to normal service.